
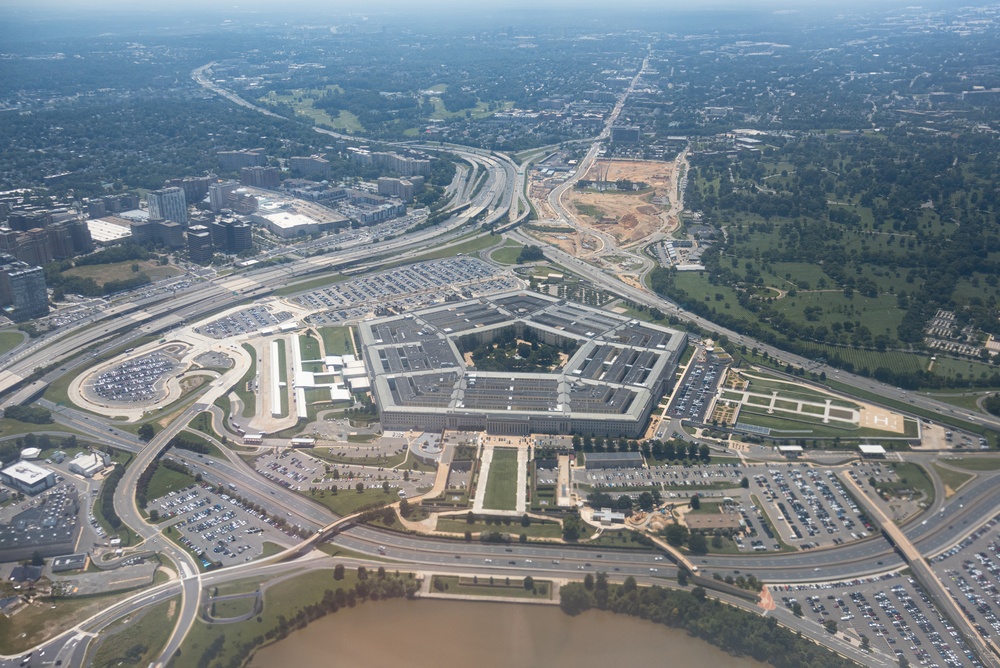
Chinese hackers hit the agency that runs America's nuclear weapons stockpile through Microsoft software in July 2025.
That same month, Pentagon brass learned Microsoft had been running a quiet arrangement inside their cloud systems since 2016.
What Hegseth found on the other end of that arrangement is why the Pentagon now calls it a breach of trust.
Microsoft's Digital Escorts Were Paid $18 an Hour
The setup was simple.
Engineers based in China and other countries handled technical work on Defense Department cloud systems.
Pentagon rules say anyone handling sensitive data has to be a U.S. citizen or permanent resident.
So Microsoft built a workaround.
It hired American "digital escorts" with security clearances to oversee the foreign engineers' work on those systems.
Plenty of them were military veterans whose main qualification was the clearance, not any skill at writing code.
Fox News reported the job paid $18 an hour.
The people on watch frequently had no way of telling whether the code coming from overseas was safe.
Microsoft's 2025 security plan for the Pentagon left out the China-based operations entirely.
Top Pentagon officials said they had no idea the arrangement existed until reporters exposed it.
That means a rogue engineer in China could have slipped something into a Pentagon system, and the American on watch would never have known.
Hegseth Shut It Down and Ordered an Audit
When the arrangement came to light in July 2025, Senator Tom Cotton demanded a list of Pentagon contractors using Chinese personnel.
Hegseth did not wait for a committee.
He said foreign engineers "should NEVER be allowed to maintain or access DOD systems."
Earlier that same week, Microsoft had defended the setup, insisting its global support staff never had direct access to customer data.
Within days, the company reversed course and announced that no China-based teams were providing technical support for Defense Department cloud services.
Microsoft also signaled it would make the same change for the Justice, Treasury and Commerce departments.
That raises an obvious question about what else was exposed.
Hegseth did not take the company's word for it.
In August 2025, he posted a video announcing a third-party audit of the escort program, at no cost to taxpayers.
"The use of Chinese nationals to service Department of Defense cloud environments? It's over," Hegseth said.
The Pentagon sent Microsoft a formal letter of concern calling the arrangement a breach of trust.
Defense Department experts opened a separate investigation into whether any of those foreign engineers tampered with the code running Pentagon systems.
Trump then signed the defense policy bill in December 2025, turning the ban into federal law.
It bars anyone from China, Russia, Iran and North Korea from direct or indirect access to Pentagon cloud systems.
Biden's Pentagon Had the Warning and Never Acted
This was not Microsoft's first rodeo with Beijing.
In 2023, Chinese state hackers used a Microsoft cloud flaw to get into the email accounts of Commerce Secretary Gina Raimondo and America's ambassador to China.
Microsoft missed it.
The State Department caught it.
Biden's own Cyber Safety Review Board ripped the company in April 2024 for a "cascade of security failures" and concluded the intrusion was preventable.
Lloyd Austin's Pentagon left the China-based support arrangement in place anyway.
The escort setup ran through three administrations, but the Biden team was the one holding a government report that called Microsoft's security culture inadequate.
Then came the July 2025 SharePoint attack, which hit hundreds of companies and government agencies on top of the nuclear stockpile agency.
A China-based engineering team supported that SharePoint product.
Microsoft insisted the team was supervised by a U.S.-based engineer.
Sound familiar?
The Audit Findings America Still Has Not Seen
Hegseth's video ordering the audit is tearing across X again, and it raises the question nobody has answered yet.
What did the investigators find?
The new law required Hegseth to brief the congressional defense committees on the crackdown by June 1, 2026, and every year after that for three years.
No audit findings have been made public.
The American people deserve those answers in plain English.
A company that let Chinese hackers walk into a cabinet secretary's inbox does not get the benefit of the doubt on military networks.
It gets an audit, a warning letter and a federal law written to close the exact loophole it exploited.
Hegseth already closed the door.
Now Microsoft has to prove nobody walked through it first.
Sources:
- Alec Schemmel, "Pentagon to Probe Microsoft's Use of Chinese Engineers on Sensitive Defense Systems, Hegseth Says," Fox News, July 18, 2025.
- Matthew Olay, "Pentagon Halts Chinese Coders Affecting DOD Cloud Systems," DOD News, August 28, 2025.
- Ross O'Keefe, "Experts Demand Investigation Into Microsoft's Alleged Use of Chinese Engineers to Maintain DOD Systems," Washington Examiner, July 16, 2025.
- Cyber Safety Review Board, "Review of the Summer 2023 Microsoft Exchange Online Intrusion," U.S. Department of Homeland Security, April 2, 2024.
Related posts:
 Kash Patel’s FBI Busted a Saudi OpenAI Engineer Over a Bug Nobody Thought to Check
 Trump Halted His Rally for Two Alaska Men Who Biden Turned Into Felons
 Ilhan Omar’s Sister Got a Federal Subpoena Hours After Judge Jeanine Pirro Revealed What Investigators Found